
Governance
Risk Management
Policy
Policy (our fundamental view)
Recognizing the various risks surrounding the NOF Group, we promote risk management initiatives with the aim of preventing the occurrence of loss risks and minimizing their impact when they do occur, thereby contributing to the achievement of management strategy targets.
- The NOF Group comprehensively identifies various management risks surrounding its business, and conducts risk assessment based on the impact and frequency of each factor in order to identify risks that need to be addressed as a priority.
- According to the characteristics of the identified risks, We work to minimize the impact on management by taking appropriate measures to reduce the impact of risks that have materialized, as well as measures to reduce the probability of occurrence.
- We work to objectively verify the effectiveness of risk countermeasures by periodically conducting risk assessments, while working to recognize and evaluate new risks.
- Under the leadership of the Risk Management Committee, we promote the risk management of the NOF Group by implementing the above risk management cycle.
Organizational setup
The Risk Management Committee, the Compliance Committee, the RC Committee, and the Quality Management Committee analyze management risks, consider countermeasures, and report to the Board of Directors. The Board of Directors receives reports and deliberates as necessary on various business risks, including those related to compliance, information management, and environment and safety, as well as confirmation and evaluation of the comprehensiveness of risks. We manage and monitor Group companies in accordance with the rules on the management of Group companies, and offer advice, as necessary, while any important matters that are deemed to materially impact our subsidiaries’ assets or profit and loss are approved by the NOF Board of Directors or the Executive Committee.
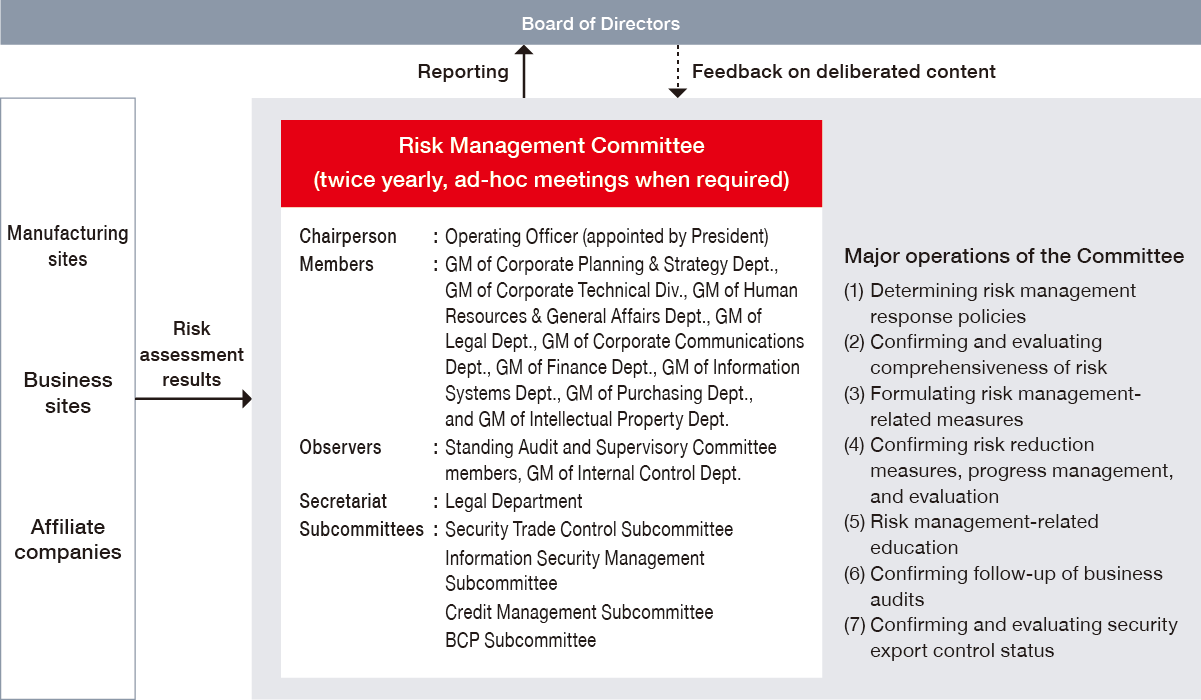
Diagram of Risk Management Committee Organization
Risk Countermeasures
Risk assessment process
The Risk Management Committee takes the lead in preparing a list of risks in consideration of the business characteristics of each department and the environment surrounding the business, including global political, economic, and social conditions. Based on this list of risks, a questionnaire is sent to each NOF site and Group company to estimate the impact and frequency of each risk. Using the results of this questionnaire, the general managers of each division carry out risk evaluations. Based on the results, the Risk Management Committee identifies the risks whose response status should be recognized by management and consults with the Board of Directors to select the key risks for monitoring.
This process is conducted once every two years, and by reviewing risk items and worst-case scenarios each time, we constantly conduct risk assessments aligned with the latest
business environment.
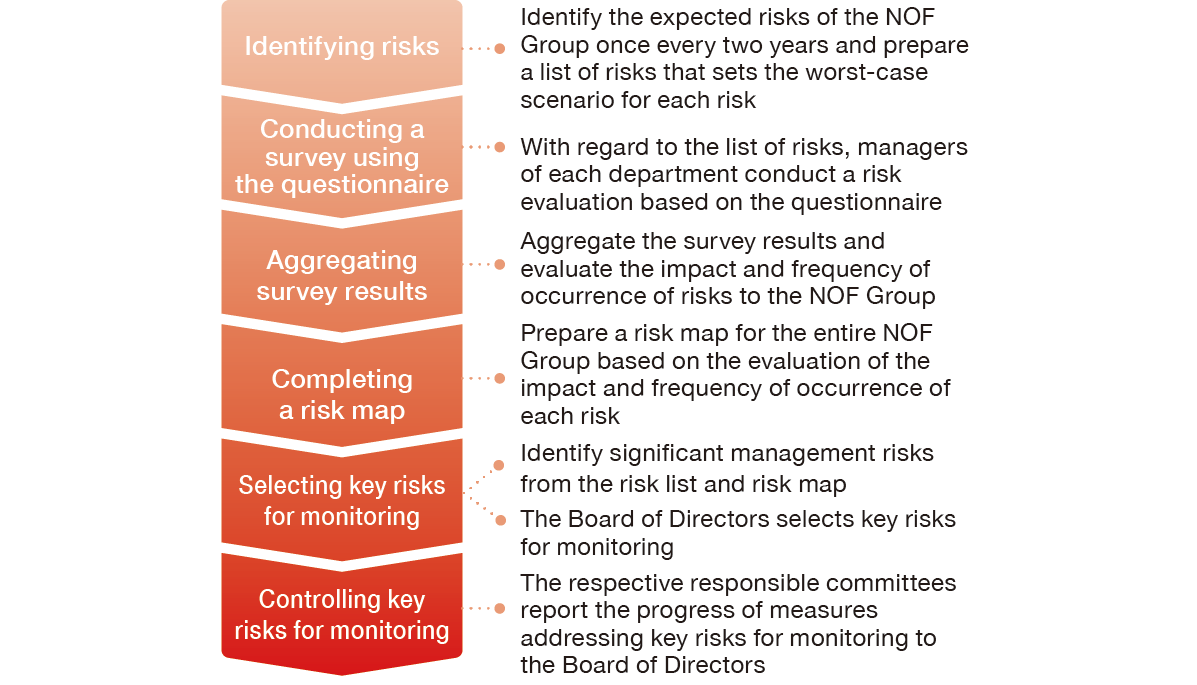
Flow of Risk Assessment
Risk map (excerpt)
The risk map is prepared based on the results of a questionnaire estimating the impact and frequency of risks at each NOF site and Group company, as well as the results of risk evaluation by managers of each department. The risk map is regularly revised and key risks for monitoring are selected in order to implement activities aimed at enhancing the NOF Group’s resilience.
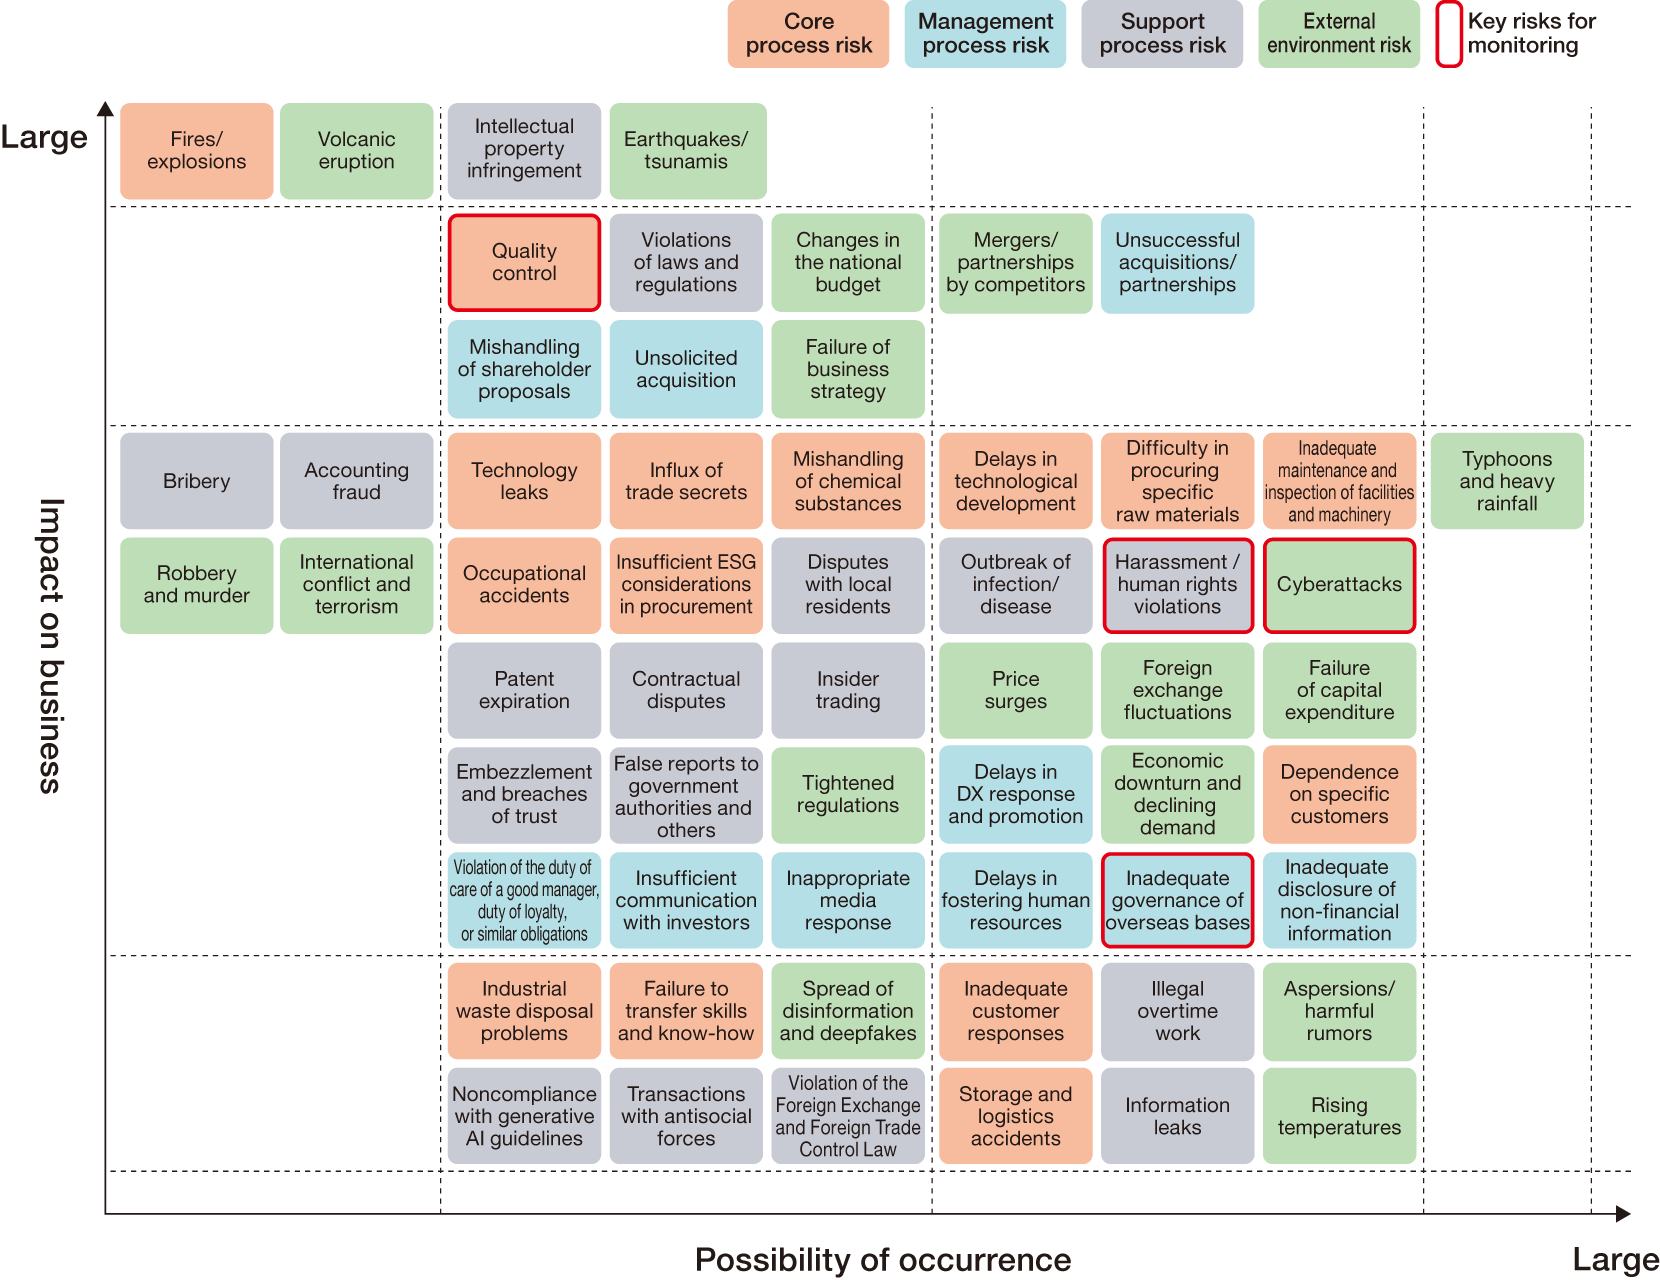
Overview and Status of Countermeasures of Key Risks for Monitoring
| Key risks for monitoring | Overview | Countermeasures |
|---|---|---|
| Harassment / human rights violations |
Possible decline in trust in the Company due to human rights abuse, such as violations of authority and sexual harassment at workplaces |
|
| Cyberattacks and information system failures | Possible information leaks and interruption of business activities, due to external attacks such as cyberattacks and information system failures |
|
| Inadequate governance of overseas bases | Possible decline in trust in the Company due to fraud, such as violations of laws and regulations, as a result of inadequate governance at overseas bases |
|
| Quality control | Possible decline in trust in the Company due to quality fraud, falsification of quality inspection results, and other situations Risk of a significant increase in workload due to rising customer quality demands |
|
Overview of Major Risks and Status of Countermeasures
| Major risk | Overview | Countermeasures |
|---|---|---|
| Technology leaks | Possible decline in the NOF Group’s competitiveness, due to leakage of technology and technical information, which allows similar products/technologies to be provided by competitors |
|
| Raw material procurement | Risk of social credibility falling due to human rights violations such as forced labor and child labor, or procurement of raw materials suspected to damage the environment |
|
| Fires / explosions | Possible casualties among employees and neighborhood residents, possible suspension of business activities, and possible compensation for damages as a result of large-scale fires and explosion accidents at plants |
|
| Intellectual property infringement, etc. | Possible compensation for damages and possible orders to suspend manufacturing and shipment, due to infringements of intellectual property rights |
|
| Violations of laws and regulations | Possible suspension of business activities and possible payments of surcharge, etc. following administrative dispositions taken in response to violations of laws and regulations, such as the Unfair Competition Prevention Act, Antimonopoly Act, Subcontract Act, Foreign Exchange and Foreign Trade Act, Chemical Substances Control Law, and Pharmaceutical and Medical Device Act |
|
| Earthquakes, tsunami, infectious diseases | Possible interruption of production activities or business activities, including sales and distribution, due to earthquakes, tsunami, or other natural disasters |
|
| Delays in talent development |
Lack of development of core talent who will be responsible for business growth, due to a delay in implementing the human resource development plan, causing a possible stall in sustainable business growth and transformation |
|
| Inadequate disclosure of non-financial information |
Possible loss of trust from stakeholders due to uncertainty about economic and environmental impact as well as social reputation |
|
Security Trade Control
Basic policy on export control
The NOF Group implements appropriate security export controls to maintain the peace and security of Japan and the international community.
- Any exports of regulated goods or other items, intermediary trade transactions, or intermediary technology transactions that violate the Foreign Exchange and Foreign Trade Act or other applicable laws shall not be conducted.
- To comply with the Foreign Exchange and Foreign Trade Act and other applicable laws and implement appropriate export controls, a person responsible for security export control shall be designated to maintain and enhance the export control system.
Export control system
To appropriately implement security export controls in accordance with laws and regulations, the NOF Group designated the President as the chief officer and established the Security Trade Control Subcommittee under the Risk Management Committee. The Subcommittee operates under the internal Security Trade Control Subcommittee Rules and related Operating Rules. The Subcommittee is chaired and overseen by an Operating Officer appointed by the President who can make judgments independently of sales. Permanent members include the General Manager of the Corporate Planning & Strategy Department, General Manager of the Corporate Technical Division, General Manager of the Legal Department, General Manager of the Intellectual Property Department of the Corporate R&D Division, and General Manager of the Explosives & Propulsion Division.
Under the export review process, export applications issued by each business division’s Sales Department receive preliminary approval from the respective Planning Office, the Subcommittee Secretariat confirms the division’s review, and the Subcommittee Chairperson grants final export approval.
The Subcommittee Secretariat also conducts annual internal audits of export reviews at business divisions, R&D divisions, and affiliated companies. Audit results are reviewed by the Subcommittee and reported to the President after deliberation by the Risk Management Committee.
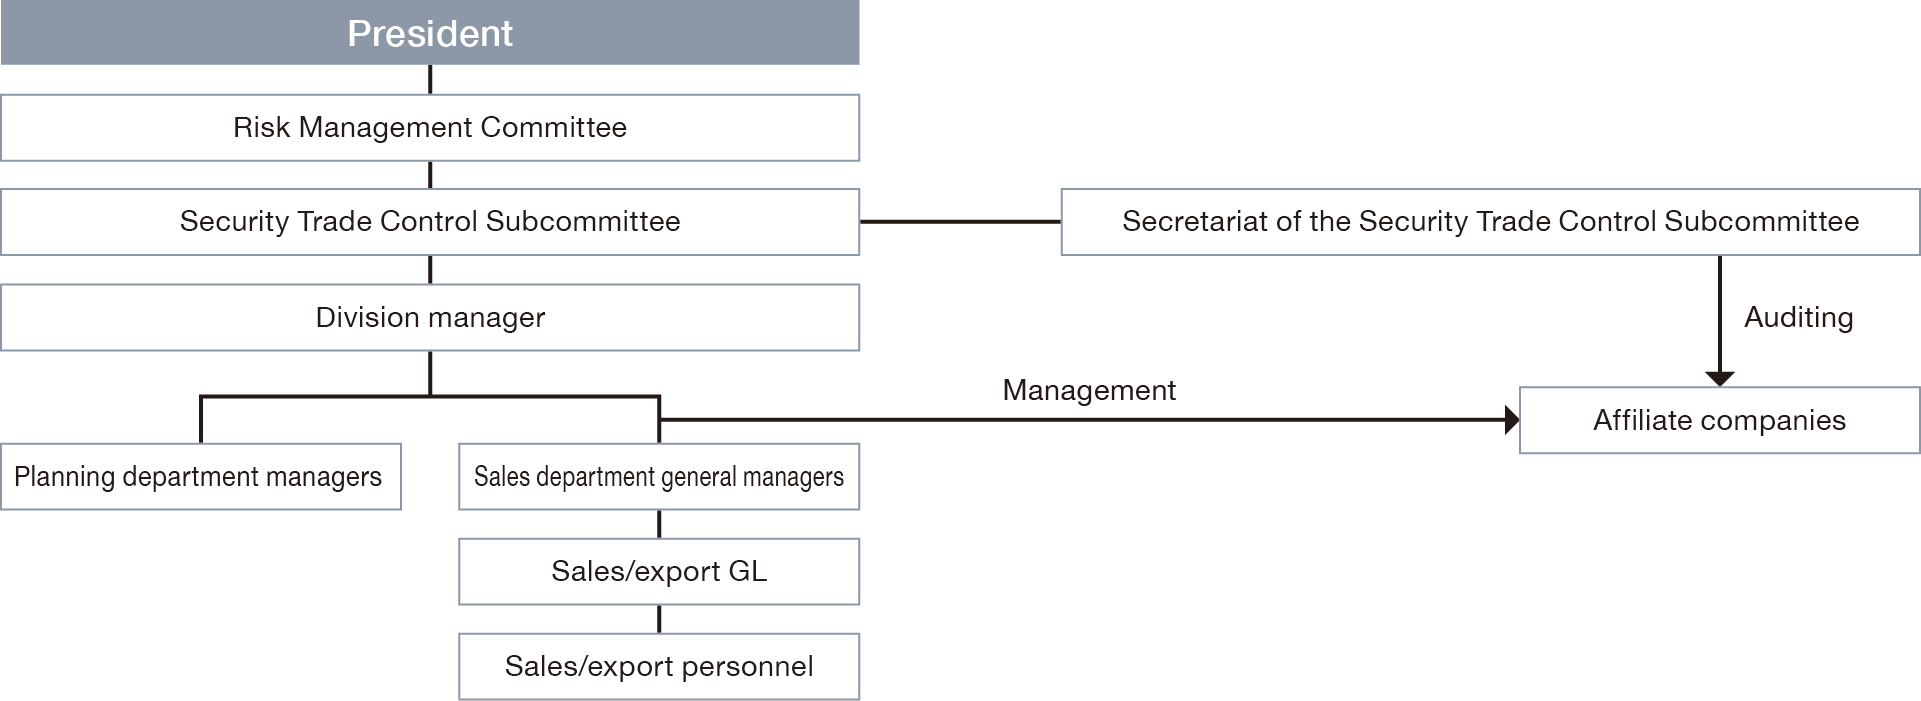
Security Trade Control Organizational Chart
Security export control at domestic affiliated companies
In accordance with the Affiliated Company Management Rules, divisions supervising affiliated companies conduct necessary monitoring and guidance to ensure thorough security export control. To ensure proper export control operations, the NOF Security Export Control Operating Standards establish systems and procedures for guidance, training, and audits of operational structures and content for applicable affiliated companies, which are implemented regularly.
Awareness, education, and other initiatives
To ensure and sustain appropriate security export controls, we conduct internal awareness activities through information dissemination and educational activities such as seminars. In FY2025, we communicated information on changes in global affairs and legal revisions. We also held seminars for NOF and affiliated companies to raise awareness of legal revisions. We will continue responding promptly to external changes while conducting internal audits and considering improvements in operational efficiency.
Business Continuity Plan (BCP)
Basic BCP*policy and management system
To minimize damage to business assets and enable the continuation or early recovery of core businesses even during emergencies such as earthquakes, tsunamis, or infectious disease outbreaks, the NOF Group has developed a business continuity plan (BCP) centered on manuals governing emergency responses. Through annual internal audits and Company-wide drills involving top management, we promote “organizational learning” and improve the embedding and effectiveness of the BCP.
We have also prepared emergency manuals for initial responses to information incidents caused by cyberattacks and safety actions by overseas expatriates.
BCP Training
| Fiscal year implemented |
Drill themes and assumed scenarios | Key verification items and issues to address |
|---|---|---|
| FY2023 | Cyberattacks and information leakage risks due to ransomware |
|
| FY2024 | Combined cyberattacks on overseas sites and geopolitical risks (heightened tensions) |
|
| FY2025 | Tokyo metropolitan earthquake causing loss of Head Office functions, combined with a leak caused by torrential rain and the spread of misinformation on social media |
|
Conducting practical drills in anticipation of diversifying risks
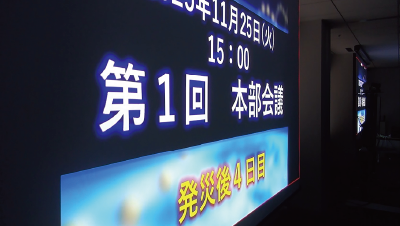
In recent years, threats surrounding companies have become increasingly diverse and complex due to more severe natural disasters, increasingly sophisticated cyberattacks, and heightened geopolitical risks. In light of these conditions, NOF’s recent BCP drills have practically simulated compound risks involving the simultaneous occurrence of multiple crises. In FY2025, we conducted a drill simulating the loss of Head Office functions due to a Tokyo metropolitan earthquake, combined with a chemical leak and the spread of misinformation on social media. The drill comprehensively verified processes for smoothly transferring authority from the affected area, initial public relations with government authorities and local residents, and risk communication.
As a result, we identified challenges such as transferring Head Office functions to a remote location, quickly detecting the spread of information on social media, and issuing timely communications. Reviewing alternative sites in the Kanto region and establishing a social listening system improved the effectiveness of our emergency BCP and our risk communication capabilities.
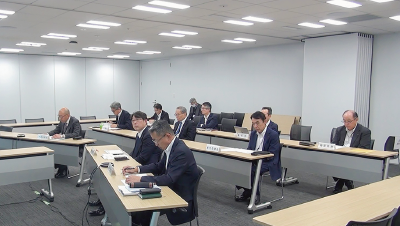
Company-wide joint BCP training
Information Security Management
Management of trade secrets and protection of personal information
The NOF Group considers information assets—including trade secrets and personal information entrusted to us by customers and business partners, or held by us, as well as systems for utilizing such information—to be important management resources in corporate activities. Based on the recognition that establishing robust information security for the information assets is essential for stable management, we have established an Information Security Policy as the basic policy for promoting the use and protection of information assets. At the same time, based on the recognition that protecting personal information is a fundamental social responsibility, we have established and published the Privacy Policy.
Under such policies, we have set forth specific measures for enhancing the levels of confidentiality, completeness, and availability of information and specific ways of handling personal information in our internal rules and manuals and are ensuring thorough dissemination and understanding within the company. Such internal rules and manuals include: Information Security Management Rules, Personal Information Protection Rules, Provisions Related to Information Systems,
Confidential Information Handling Manual, and Information Equipment Handling Manual.
NOF Group Information Security Policy
The NOF Group considers information such as trade secrets and personal information entrusted to us by customers or business partners, or held by the Group, as well as systems, etc. for utilizing such information (below, “information assets”) as important management resources in corporate activities. Based on the recognition that establishing robust information security for information assets is essential for stable management, we have established the below Policy and ensure compliance therewith.
- The NOF Group shall develop the information security system to further strengthen the management function of information assets.
- In order to protect the information assets from leakage, falsification, and destruction, the NOF Group shall provide information security education for employees, develop regulations, and implement technical measures for information systems.
- The NOF Group shall comply with laws, regulations, codes, and contractual obligations related to information security.
- In the event of an information security incident, the NOF Group shall respond promptly and appropriately to each incident and prevent a recurrence.
- The NOF Group shall maintain and continually improve these efforts in this Policy.
Management system
In the internal organizational aspect, the Information Security Management Subcommittee is set up to deliberate and make decisions on important matters related to information security. Under the Information Security Management Supervisor, who is the chairperson of the Subcommittee, document information security management supervisors, electronic information and information system security management supervisors, personal information complaints handling supervisors, as well as a person responsible for management at each division, site, and department are appointed to manage the implementation of specific measures. Against threats such as unauthorized access from external, information leakage, falsification, and destruction, appropriate and reasonable security measures are implemented. In addition, NOF continually reviews and strives to improve the information security management and personal information protection systems and measures through internal audits.
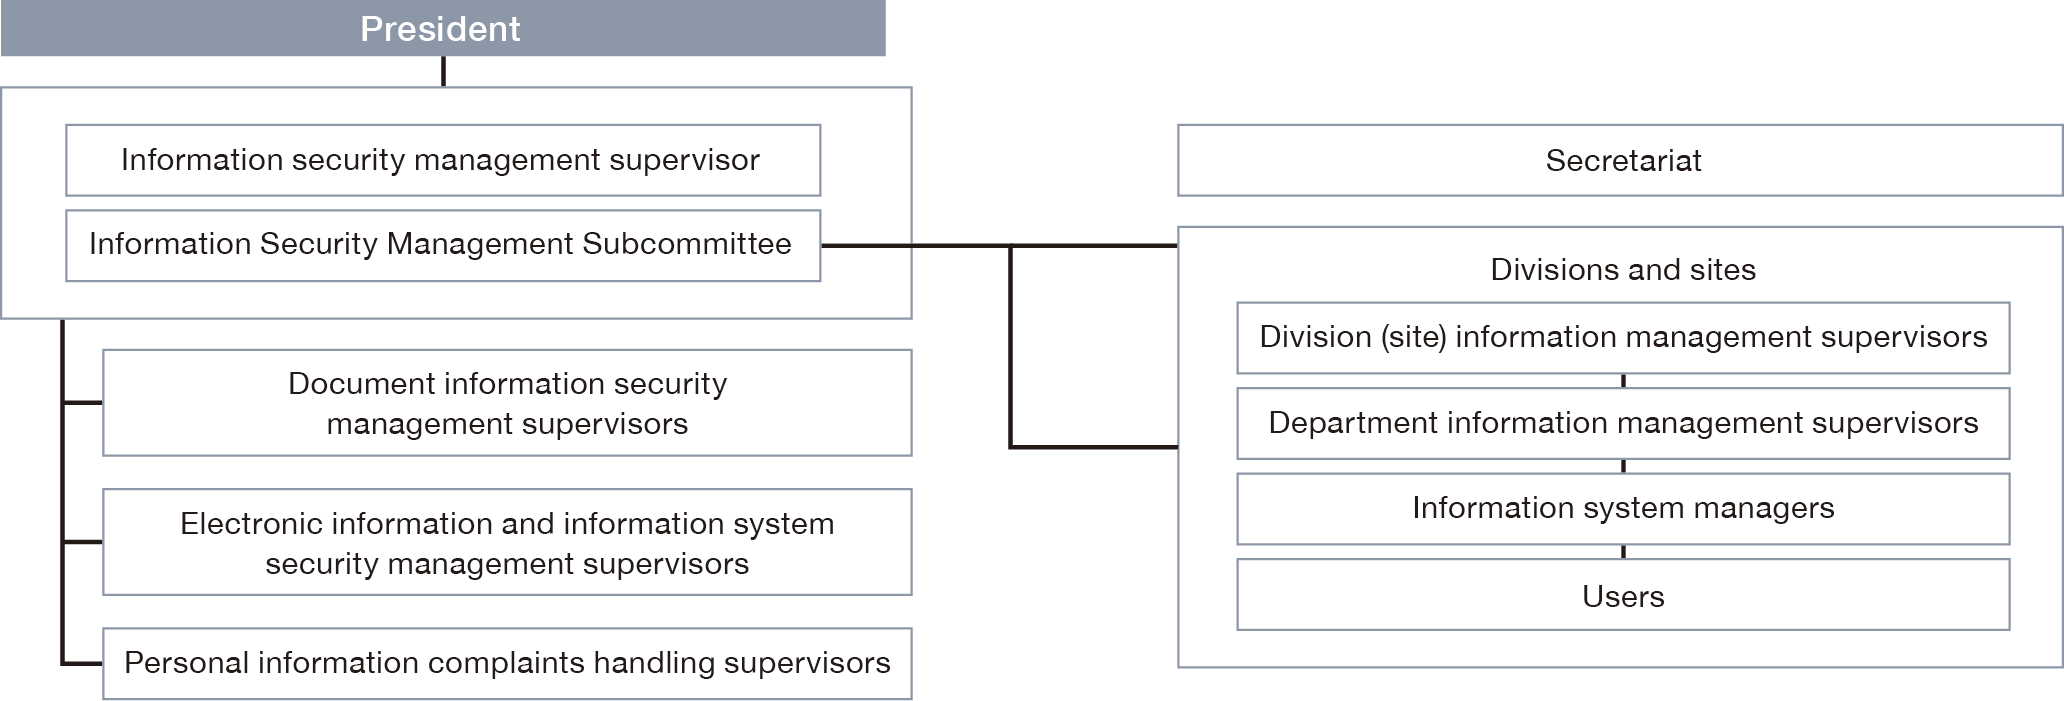
Diagram of NOF’s Information Security Management System
Risks and opportunities
The NOF Group recognizes the risks of business interruption and loss of trust due to cyberattacks and leaks of confidential or personal information, while viewing stronger information asset management as an opportunity to enhance competitiveness, earn customer trust, and improve employees’ security awareness. To both reduce risks and maximize opportunities, we implement risk-based measures and continuous monitoring and education.
Risks and Opportunities in Information Security
| Risks and opportunities | Details | Countermeasures |
|---|---|---|
| Risks |
|
|
| Opportunities |
|
- |
Number of Information Security Incidents [Covered organizations:NOF] (Number)
| FY2023 | FY2024 | FY2025 | |
|---|---|---|---|
| Number of incidents that occurred | 0 | 0 | 0 |